Welcome, please join me.
This is a space where curiosity meets cybersecurity. Whether you're here to learn the fundamentals of staying safe online, explore the evolving world of AI security, or find practical advice to grow your career in the industry — you're in the right place. I created this site to share what I've learned over nine years in the field, break down complex topics into concepts that stick, and hopefully pass along some of the passion that keeps me learning every day. Pull up a chair, explore, and let's make security make sense — together.
Knowledge is power. Teaching is my superpower.
Teaching, when done with intention, goes far beyond sharing information. It shapes how people think, how they make decisions, and how they act when it matters most. Real teaching doesn't aim for memorization — it builds understanding, confidence, and the ability to navigate complexity with clarity.
It takes empathy to meet people where they are. Clarity to simplify without stripping away meaning. And purpose — to connect every concept to something real, something that changes how a person shows up in the world.
What makes teaching powerful is that it doesn't stop with one person. It ripples outward — into teams, into decisions, into outcomes far beyond your immediate reach. That's why I believe in developing thinkers, not followers. Empowering, not overwhelming. Creating independence, not dependence. At its best, teaching is a multiplier — it turns knowledge into capability, and capability into lasting impact.
Explore the free resources
-
![Identity as the New Control Plane]()
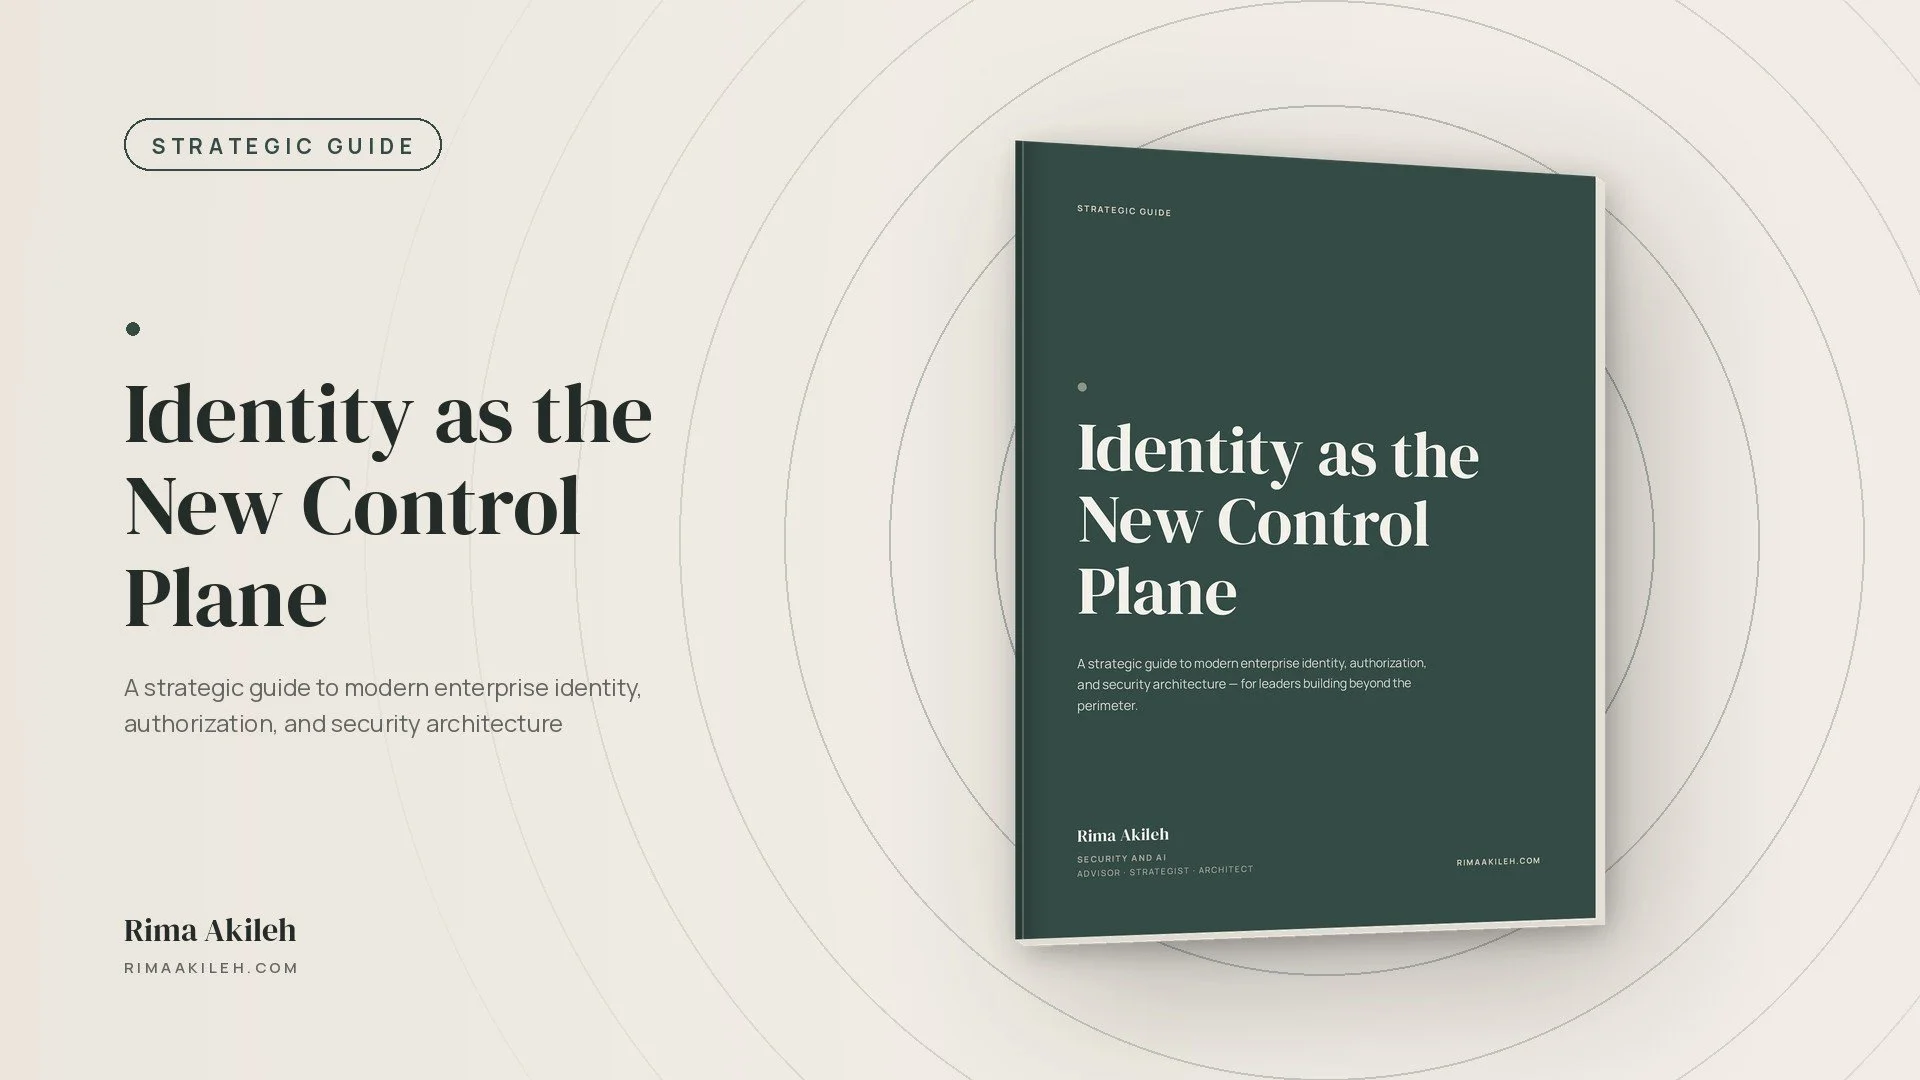
Identity as the New Control Plane
Why identity has replaced the network perimeter as the center of enterprise security. Covers context-aware access, delegated authority, and how to design an identity control plane.
-
![AI Security for the Enterprise]()
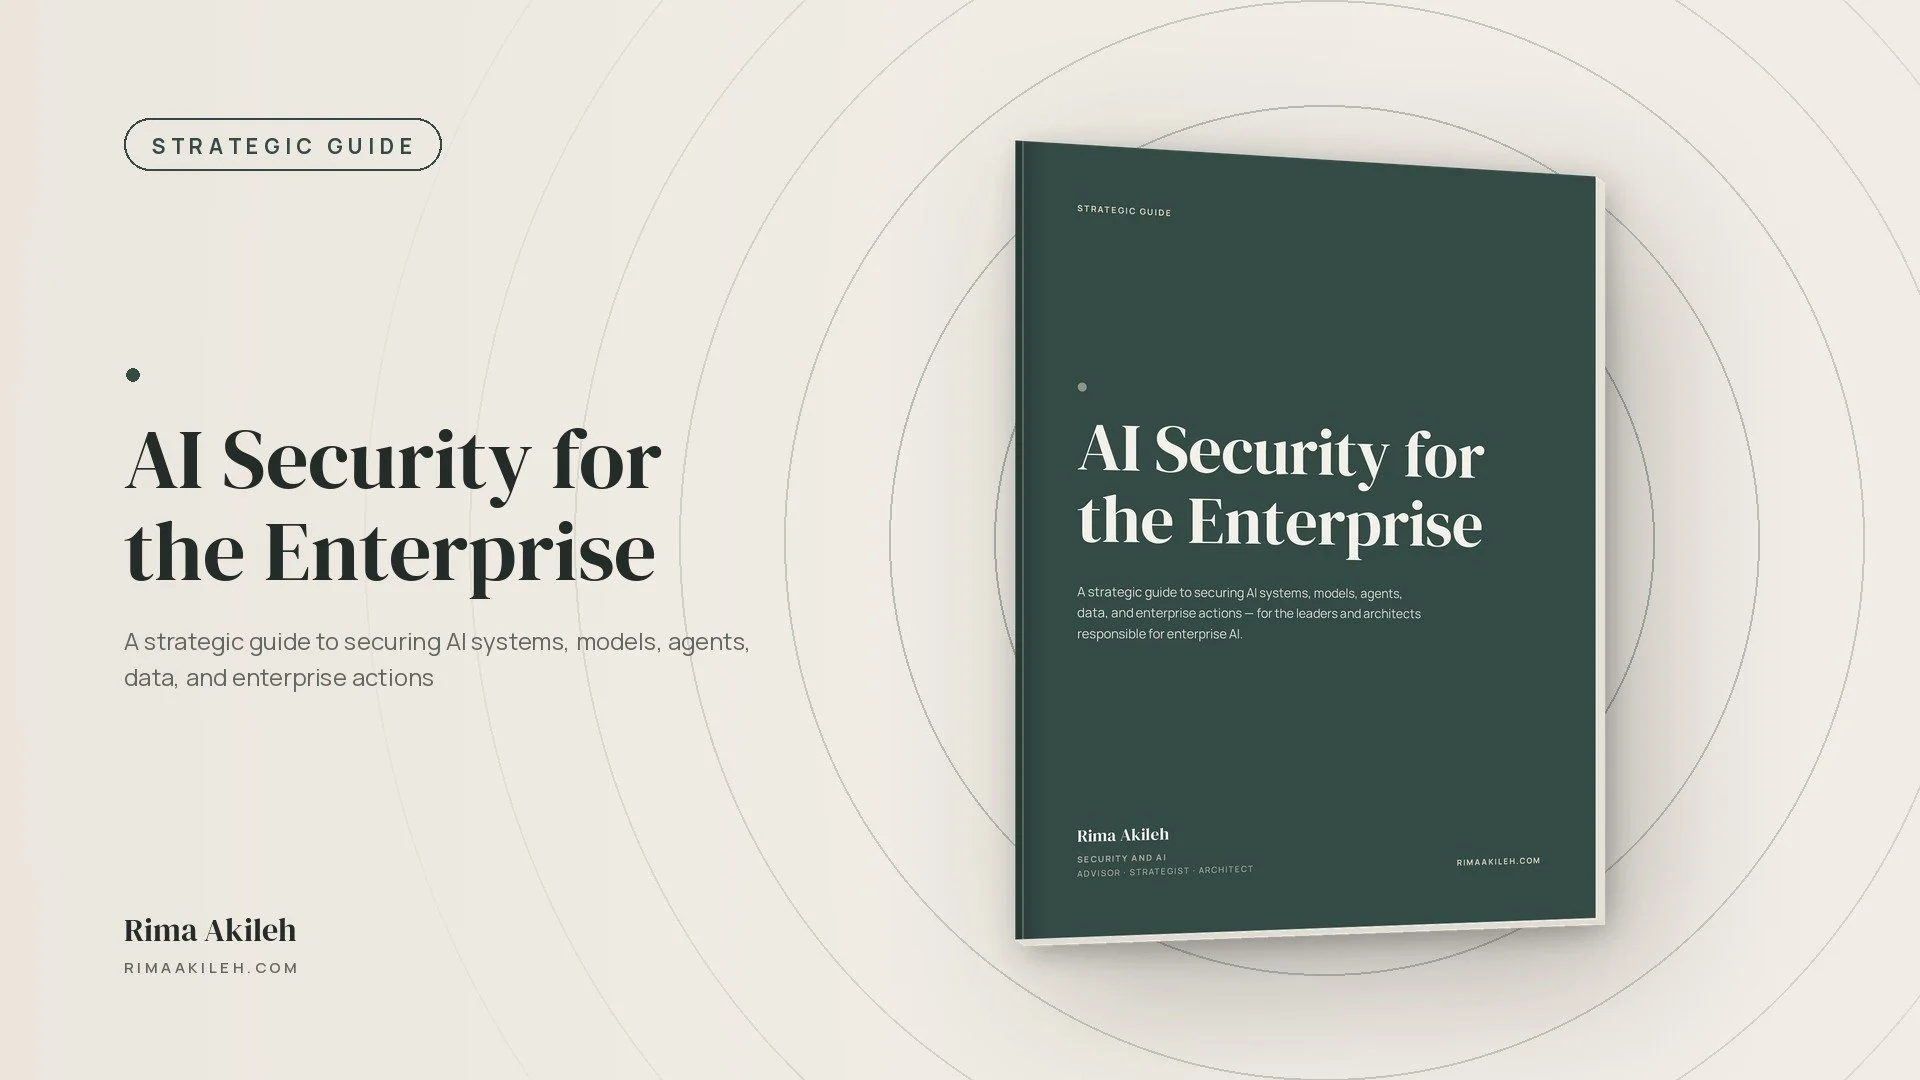
AI Security for the Enterprise
How to secure the whole AI system, not just the model: data, agents, outputs and actions. Covers the AI threat model, human oversight, AI security operations, and supply chain risk.
-
![AI Agent Identity & Access]()
AI Agent Identity & Access
A phased playbook for giving AI agents real identities, delegated authority and least-privilege access. Covers agent inventory, credentials, tool and connector access, session controls, and lifecycle management.
-
![Zero Trust Transformation]()
Zero Trust Transformation
A step-by-step plan for putting Zero Trust into practice across access, trust, segmentation and policy. Covers trust assessment, a prioritized roadmap, and application and network transformation.
ABOUT ME
I picked up a clipboard when I was eight years old — coordinating a talent show, arranging timelines, organizing people. That clipboard was the symbol that helped me bring structure to complexity and followed me along my career: into instructional design, consulting, event planning, and later into cybersecurity. I kept solving different puzzles in different rooms.
Over the past nine years, I’ve worked across both sides of the security equation. On the offensive side, I’ve communicated risk from penetration tests and security assessments, learned how attackers think, analyzed third-party risk, and built security maps. On the defensive side, I’ve built programs in Data Loss Prevention, Incident Response, Identity and Access Management, GRC, and Security Design Reviews. What I found along the way was a gap that too few people were filling — the space between the technical team and the boardroom. I became the person who could translate complexity and provide context for business and technology.
Today, I’m focused on the security challenges that will define the next decade: securing AI tools from the ground up, managing AI integrations across enterprise environments, and solving access management for non-human identities. But no matter how technical the problem gets, my approach stays the same — I don’t take away someone’s choice. I educate them about the consequences so they can make informed decisions. That’s how lasting security culture gets built.